A practical cost framework for independent pharmacy operators
For an independent pharmacy, a cybersecurity assessment is not an abstract technology expense. It is a fixed-cost way to find the gaps that could interrupt dispensing, claims processing, ordering, payment, communication, and access to essential records. One day of downtime can put several of those workflows on hold at once, while the cost of the interruption continues to build.
The exact impact will differ by pharmacy. Script volume, staffing, point-of-sale activity, delivery operations, system dependencies, and recovery time all matter. But the comparison is still practical: an assessment has a known scope and cost, while downtime produces a stack of uncertain costs that can extend beyond the outage itself. Compare the assessment with the cost of disruption, not with a zero-dollar assumption that nothing will happen.
Key Takeaways
- A pharmacy cybersecurity assessment creates a baseline of the pharmacy’s current security posture and identifies practical priorities before an incident or outage forces the issue.
- One day of downtime can affect prescription workflow, claims, point-of-sale activity, inventory, delivery, labor, patient communication, and recovery work at the same time.
- The most useful downtime estimate is pharmacy-specific. It should include margin at risk, labor disruption, vendor and recovery costs, backlog, and patient service effects.
- An assessment does not guarantee security or compliance. Its value is clearer visibility, better prioritization, and more informed decisions.
- CommUnity Guard starts with a fixed-cost, time-bound assessment and provides written findings, plain-language explanations, and prioritized recommendations. Any follow-on support is optional and based on the pharmacy’s needs.
What Is a Pharmacy Cybersecurity Assessment?
A pharmacy cybersecurity assessment is a structured review of technology, access, updates, safeguards, and operational dependencies. It creates a current-state baseline, identifies gaps, and organizes recommended actions by urgency and business impact.
For pharmacy operators, the point is not to become an IT expert. The point is to answer a management question: Where are we relying on assumptions, and what should we address first?
Why Does One Day of Pharmacy Downtime Cost So Much?
A pharmacy depends on a connected operating environment. Prescription intake, adjudication, dispensing, inventory, ordering, payment, phones, e-prescribing, delivery, and reporting may rely on different systems, vendors, devices, and connections.
When one critical dependency fails, the effect can spread. Staff may be present but unable to complete normal tasks. Patients still arrive, phones still ring, and prescriptions continue to enter the queue. After systems return, the team may still need to reconcile transactions and process the backlog.
Cybersecurity is therefore part of business continuity. A cyber incident is not the only cause of downtime, but weak security practices, outdated systems, excessive access, untested backups, or unclear response roles can make an interruption more likely, harder to contain, or slower to recover from.
The HIPAA Security Rule requires covered entities and business associates to assess potential risks and vulnerabilities to electronic protected health information. It also includes contingency planning specifications addressing backup, disaster recovery, emergency-mode operations, testing, and critical applications and data.[1][2] The operating principle is straightforward: understand risk and recovery needs before normal operations are disrupted.
What Actually Goes Into the Cost of a Downtime Day?
Daily revenue does not tell the whole story. Some transactions may be delayed and recovered; others may be transferred, abandoned, or lost. A better estimate separates costs into categories the operator can evaluate honestly.
1. Prescription and Front-End Margin at Risk
Start with the work the pharmacy normally completes in a day. Estimate prescription gross profit or contribution margin that may be delayed or lost, then add affected front-end and point-of-sale margin. Use margin rather than total revenue when the goal is to estimate economic impact.
A simple starting formula is:
Daily margin at risk = affected prescriptions x average gross profit per prescription + affected front-end gross profit
Use a realistic range rather than assuming every prescription disappears. A brief interruption may delay fills; a longer one may cause transfers, abandonment, or missed delivery windows.
2. Paid Labor With Reduced Throughput
Payroll continues during an outage. Pharmacists, technicians, cashiers, drivers, and managers may spend the day answering questions, documenting pending work, contacting vendors, using approved downtime procedures, and managing a growing queue.
That labor may be essential to patient service and recovery, but normal productive capacity is reduced. Include regular wages, overtime, schedule extensions, and any temporary coverage needed during catch-up.
3. Recovery and Technical Expense
An interruption may require after-hours vendor support, emergency IT assistance, equipment or network work, data restoration, or professional consultation. These uncertain expenses arrive when the pharmacy has little time to compare options.
An assessment changes the timing of the decision. It helps the owner identify priorities during normal operations, when work can be scoped, scheduled, and budgeted.
4. Backlog and Reconciliation
Recovery is not complete when the screen turns back on. The pharmacy may need to verify information, reconcile transactions, confirm claims status, review queued prescriptions, update deliveries, and document what occurred.
Backlog can reduce throughput the next day and create overtime even when the technical outage lasted only a few hours. For the cost comparison, estimate the recovery tail as well as the interruption itself.
5. Patient Service and Relationship Effects
Avoid assigning a dramatic dollar amount to trust, but recognize the operational effect. Patients may face delays, extra trips, transferred prescriptions, or uncertainty about medication availability.
Treat this as a service-risk category rather than an inflated financial claim. Ask which patient groups, delivery routes, facilities, or time-sensitive medications would require the most attention during an outage.
How Can a Pharmacy Estimate Its Own Downtime Cost?
Use a range instead of chasing a falsely precise number. Build a conservative case, an expected case, and a high-impact case. The exercise can be completed with information the pharmacy already tracks.
For each scenario, estimate:
- Prescription and front-end margin delayed or lost
- Regular labor operating below normal capacity
- Overtime and catch-up labor
- Emergency vendor, equipment, and recovery expense
- Delivery disruption and added communication work
- Backlog carried into the next operating day
- Potential prescription transfers or patient attrition, stated conservatively
Then ask how long the pharmacy could operate using its approved downtime procedures. A four-hour outage, a full operating day, and a multi-day recovery produce very different results.
The result is a decision tool, not a prediction. If the conservative cost of one interrupted day exceeds the known assessment cost, the assessment becomes easier to evaluate as operational risk management.
Why Is an Assessment a Better First Step Than Buying More Technology?
Pharmacies often already have security products, an IT vendor, or controls added over time. The question is whether those pieces are configured, maintained, and coordinated around actual risk.
Buying another tool before reviewing the environment can add cost without resolving the most important gap. An assessment starts with visibility. It asks what exists, how it is being used, where responsibility sits, and which weaknesses have the greatest operational consequence.
The NIST Cybersecurity Framework 2.0 organizes cybersecurity outcomes across six functions: Govern, Identify, Protect, Detect, Respond, and Recover.[3] In plain language, leadership assigns responsibility, identifies critical dependencies, applies safeguards, watches for problems, defines response roles, and prepares to restore priority work.
An assessment helps establish where the pharmacy stands across that sequence. It can also reveal when a control exists on paper but has not been verified in practice.
What Should Pharmacy Operators Expect From an Assessment?
The CommUnity Guard Assessment is designed as a fixed-cost, time-bound first step. It reviews the pharmacy’s security posture and identifies gaps related to security practices, updates, access controls, and overall risk exposure.
The pharmacy receives:
- A written cybersecurity assessment report
- A plain-language explanation of the findings
- Prioritized remediation recommendations
- A distinction between risks needing more immediate attention and longer-term improvements
The output should help leadership make decisions. A useful finding explains the issue, why it matters operationally, the recommended next step, and its relative priority.
An assessment is also not a commitment to a large technology project. Based on the findings, a pharmacy may choose to address items internally, work with an existing provider, or consider optional support from CommUnity Guard. The next step should match the environment and the pharmacy’s priorities.
What an Assessment Does Not Do
Clear expectations are part of good risk management. A cybersecurity assessment does not:
- Guarantee that a cyber incident or outage will never occur
- Certify legal or regulatory compliance by itself
- Replace an incident response or business continuity plan
- Prove that a backup can be restored unless restoration is actually tested
- Eliminate the need for staff awareness, maintenance, and periodic review
- Require the pharmacy to buy every recommended service at once
Its purpose is to replace uncertainty with a clearer baseline and a prioritized plan. That is valuable because pharmacy operators rarely have unlimited time or budget. The practical question is not whether every risk can be removed. It is which actions reduce meaningful exposure first.
Which Findings Most Directly Affect Business Continuity?
Every pharmacy environment is different, but several assessment areas commonly connect security with day-to-day continuity.
Access and Account Control
The pharmacy should know who can access critical systems, whether former staff accounts are removed promptly, when shared credentials are used, and how privileged access is controlled.
Updates and Unsupported Systems
Leadership needs to know who is responsible for updates, whether they are occurring, and how changes are tested or scheduled around pharmacy operations.
Backup and Restore Readiness
A statement that data is “backed up” is only the beginning. Operators should know what is backed up, where copies are stored, how frequently backups occur, who can initiate recovery, and whether restoration has been tested. CISA’s ransomware guidance emphasizes offline or otherwise separated backups and regular testing of backup availability and integrity.[4]
Vendor and System Dependencies
An assessment can map dependencies across dispensing, claims connectivity, internet, phones, payment, security, delivery, and support, then clarify which contact should be called first.
Response Roles and Communication
Define who makes operating decisions, contacts vendors, communicates with staff and patients, documents events, and escalates privacy or security concerns. Keep contact information available when primary systems are not.
How Can a Pharmacy Get More Value From the Assessment?
Connect the assessment to operating decisions. Before the review, list what must keep working and what has caused trouble before.
Bring the following questions to the assessment:
- Which five workflows are most critical to a normal operating day?
- How long can each workflow be unavailable before patient service or business performance is materially affected?
- Who has authority to shift into downtime procedures?
- Where are vendor contacts and recovery instructions stored?
- When were backups last restored in a test?
After the assessment, assign an owner and target date to each accepted recommendation. Begin with items affecting critical operations, access, recovery, or known exposure. Document deferred risks and when they will be reconsidered.
This turns the report into a management tool instead of a file that sits on a shelf.
A Practical Business Continuity Checklist for Pharmacy Operators
Pair the assessment with a continuity plan simple enough to follow under pressure.
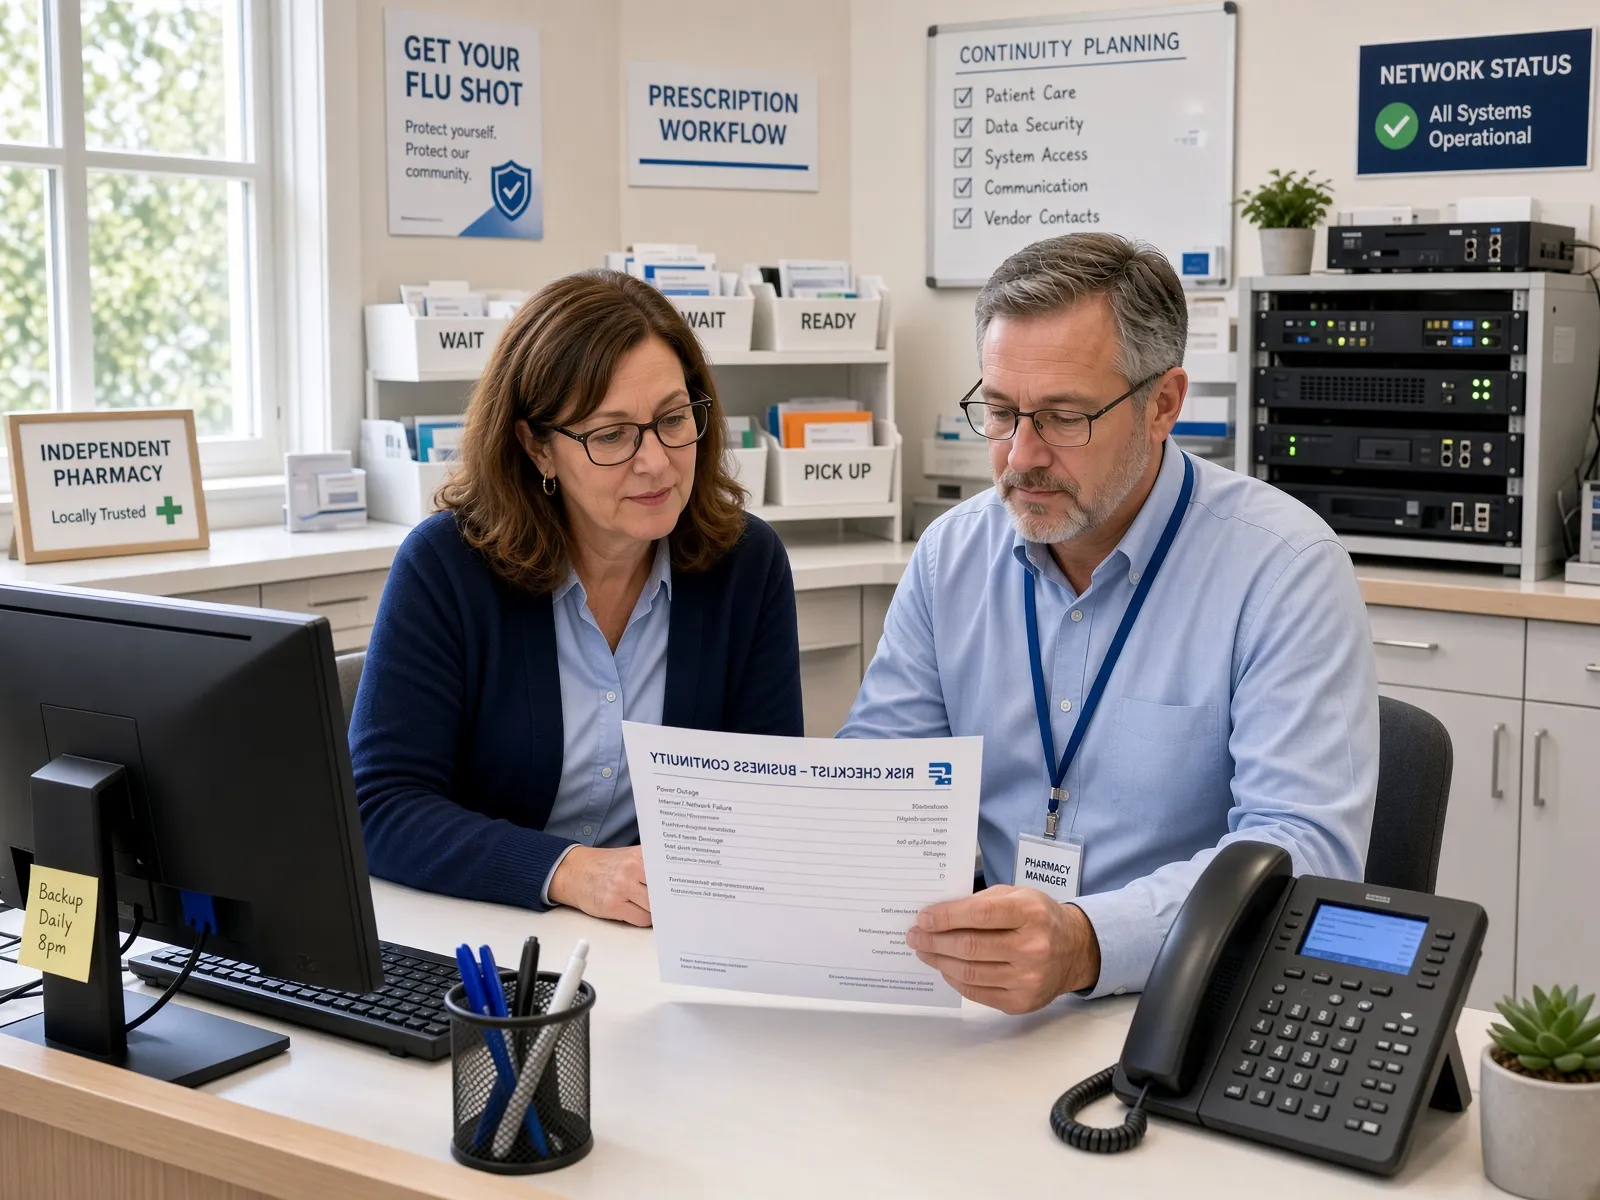
- List critical workflows in recovery order, including dispensing, claims, point of sale, ordering, phones, delivery, and key reporting.
- Document approved downtime procedures with the relevant system vendors and pharmacy leadership. Do not improvise processes that could create patient-safety, privacy, billing, or recordkeeping problems.
- Maintain an offline or otherwise independently accessible contact list for staff, system vendors, internet and phone providers, payment support, insurance, legal counsel, and other escalation resources.
- Verify backup scope and responsibility, then schedule restoration tests appropriate to the pharmacy’s environment.
- Prepare plain-language communication templates for staff, patients, prescribers, facilities, and other partners.
- Practice a short tabletop scenario and update the plan when roles, vendors, systems, or locations change.
The plan should support the first sound decisions without depending on memory or an unavailable system.
Frequently Asked Questions
How much does one day of pharmacy downtime cost?
There is no responsible universal figure. Estimate your pharmacy’s prescription and front-end margin at risk, paid labor at reduced throughput, overtime, emergency technical costs, delivery disruption, patient communication, and backlog. Use conservative, expected, and high-impact scenarios.
Is a cybersecurity assessment required for a pharmacy?
Pharmacies that are HIPAA covered entities must comply with applicable HIPAA Security Rule requirements, including risk analysis of electronic protected health information. Whether a specific commercial assessment satisfies an obligation depends on its scope and the pharmacy’s circumstances. The assessment should support, not replace, qualified legal and compliance guidance.[1]
Will a cybersecurity assessment prevent downtime?
No assessment can guarantee uninterrupted operations. It can identify weaknesses, clarify dependencies, prioritize improvements, and strengthen preparation, which can help reduce the likelihood or operational impact of some disruptions.
What is the difference between a cybersecurity assessment and a penetration test?
A cybersecurity assessment reviews the broader security posture, practices, responsibilities, controls, and operational risks. A penetration test is a more technical exercise that attempts to identify exploitable weaknesses within an agreed scope. One does not automatically substitute for the other.
How often should a pharmacy review cybersecurity risk?
Review should be ongoing and should occur when the environment changes, such as adding a location, replacing a core system, changing vendors, adopting new connectivity, or experiencing an incident. A regular formal review cycle can help leadership verify that earlier findings were addressed and that new risks have been considered.
What should a pharmacy do first after receiving assessment results?
Confirm the highest-priority findings, assign an accountable owner, choose realistic target dates, and address items tied to critical operations, access, known exposure, and recovery capability. Ask for plain-language clarification before approving technical work you do not understand.
The Lower-Cost Decision Is the One Made Before Downtime
A cybersecurity assessment and a day of downtime are not equivalent purchases. One is planned, scoped, and designed to create clarity. The other is an interruption that can combine lost or delayed margin, reduced throughput, recovery expense, backlog, and patient service challenges in a single operating day.
Independent pharmacy owners do not need a fear-based prediction to make a sound decision. They need to understand their own dependencies, estimate the operational cost of losing them, and verify whether current protections and recovery plans match the pharmacy’s actual risk.
CommUnity Guard provides a pharmacy-specific, fixed-cost assessment with a written report, plain-language findings, and prioritized recommendations. Start by learning what the assessment covers and whether it is the right next step for your pharmacy. Clarity first. Solutions only if you need them.
Sources
1. U.S. Department of Health and Human Services, “Guidance on Risk Analysis Requirements Under the HIPAA Security Rule,”
2. Electronic Code of Federal Regulations, 45 C.F.R. § 164.308, Administrative Safeguards
3. National Institute of Standards and Technology, “The NIST Cybersecurity Framework (CSF) 2.0,”
4. Cybersecurity and Infrastructure Security Agency, “#StopRansomware Guide,”